Website for Cybersecurity Companies: How to Generate Enterprise Leads from the US and Europe

Cybersecurity companies face a difficult website problem.
Their services may be technically strong, the team may have deep expertise, and the company may be capable of handling serious infrastructure, compliance, cloud security, penetration testing, or managed security projects.
But the website often fails to communicate that expertise to the people who actually approve enterprise contracts.
A technical buyer may understand the terminology. A CFO, COO, procurement manager, or company owner may not. At the same time, simplifying the message too much can make the cybersecurity provider look generic.
For companies targeting enterprise clients in the United States and Europe, the website therefore has to perform several jobs at once: explain technical capability, reduce perceived risk, prove credibility, support a long buying cycle, and generate qualified conversations.
This article explains how a cybersecurity company website should be structured when the goal is not simply traffic, but serious B2B opportunities.
Why Cybersecurity Websites Are Harder to Build Than Typical B2B Websites
Cybersecurity is not an impulse purchase.
A potential client may be evaluating:
- technical competence;
- risk management;
- data handling;
- regulatory implications;
- response capability;
- industry experience;
- vendor reliability;
- long-term support.
The buyer is not only asking, “Can this company provide the service?”
They are also asking:
“Can we trust this company with systems, data, infrastructure, and business continuity?”
This makes trust architecture especially important.
A cybersecurity website that looks polished but provides little evidence may create more questions than confidence.
The Typical Problem: Technical Expertise Hidden Behind Generic Marketing
Many cybersecurity websites use broad language such as:
- Protect your digital future;
- Advanced security solutions;
- Secure your business;
- Your trusted cybersecurity partner;
- Next-generation protection.
These phrases are not necessarily wrong, but almost any cybersecurity company can use them.
An enterprise buyer needs more precision.
They want to know:
- what type of security problems you solve;
- which environments you work with;
- which organizations you are best suited for;
- how your engagement process works;
- what experience supports your claims;
- what happens after an incident or discovery;
- how you communicate risk to management.
The website should turn technical capability into a business case.
Start with Positioning: What Type of Cybersecurity Company Are You?
Trying to rank and convert for “cybersecurity services” is usually too broad.
The market becomes much more understandable when the website communicates specialization.
Examples of narrower positioning include:
- managed security for SaaS companies;
- penetration testing for fintech platforms;
- cloud security assessments for AWS-based businesses;
- security audits for European ecommerce companies;
- vulnerability management for mid-market B2B organizations;
- security consulting for companies preparing for enterprise procurement;
- incident response support for distributed organizations.
The objective is not to artificially reduce the business scope.
The objective is to help the right buyer immediately recognize relevance.
A broad company can still have multiple specialized landing pages for different services, risks, industries, and environments.
Homepage: Communicate Risk, Audience and Capability Quickly
The homepage should not begin with a long technical explanation.
It should establish context quickly.
A strong first screen usually answers:
- Who do you protect?
- What type of risk do you reduce?
- What is your specialization?
- What should a qualified visitor do next?
For example, instead of:
Advanced Cybersecurity Solutions for Modern Businesses
a company could use more specific positioning such as:
Security Assessments and Penetration Testing for SaaS Companies Selling to Enterprise Clients
The second version immediately communicates service type, audience, and business context.
Below the first screen, the homepage can then support that positioning with proof, services, use cases, case studies, industries, and a clear consultation path.
Service Pages Should Match Enterprise Buying Intent
A cybersecurity website should not place every service into one generic page.
Each high-value service deserves a dedicated commercial page.
Depending on the company, this may include:
- Penetration Testing;
- Web Application Security Testing;
- Cloud Security Assessment;
- Security Architecture Review;
- Vulnerability Assessment;
- Managed Detection and Response;
- Incident Response;
- Security Consulting;
- Compliance Readiness Support;
- Security Audit for M&A or Enterprise Procurement.
Each page should answer more than “what the service is.”
It should explain:
- when a company typically needs the service;
- which risks it addresses;
- what is included;
- how the engagement works;
- what the client receives;
- what happens after findings are delivered;
- which types of organizations are a good fit.
This makes the page useful both for search and for internal buying discussions.
Do Not Write Only for Security Engineers
One of the biggest mistakes on cybersecurity websites is writing every page for highly technical specialists.
Technical depth is important, but enterprise purchases often involve several stakeholders.
The website may be reviewed by:
- CISO;
- CTO;
- IT manager;
- security engineer;
- CEO;
- COO;
- legal team;
- procurement;
- compliance team.
Each stakeholder looks at the project differently.
A security engineer may care about methodology and scope.
A CTO may care about operational risk.
A procurement manager may care about process, documentation, and supplier reliability.
An executive may care about business exposure and continuity.
A strong service page should therefore provide enough technical detail for specialists while still making the business value understandable to non-specialists.
Show Methodology Instead of Making Generic Claims
Cybersecurity buyers are naturally skeptical.
Claims such as “industry-leading security expertise” are weak unless supported by evidence.
A better website explains how the team works.
For example, a penetration testing page could outline:
- scoping and environment review;
- attack surface analysis;
- manual and automated testing;
- validation of findings;
- risk prioritization;
- report delivery;
- technical review with the client team;
- retesting where included.
This gives the buyer something concrete to evaluate.
Methodology demonstrates maturity more effectively than marketing adjectives.
Case Studies Should Focus on Risk and Resolution
Cybersecurity case studies require care because client information may be sensitive.
But this does not mean the website should have no proof.
An anonymized case study can still explain:
- the type of organization;
- the original security concern;
- the scope of the assessment;
- the types of weaknesses discovered;
- how risk was prioritized;
- what remediation approach was used;
- what changed after the engagement.
The case study does not need to reveal exploitable details.
The purpose is to show how the team thinks and works.
For enterprise buyers, this can be much more persuasive than a list of logos without context.
Create Industry-Specific Landing Pages Carefully
Cybersecurity requirements differ between industries.
This creates an opportunity for targeted landing pages such as:
- Cybersecurity Services for Fintech Companies;
- Penetration Testing for SaaS Platforms;
- Security Audits for Healthcare Software Companies;
- Cloud Security for European Ecommerce Businesses;
- Security Assessments for B2B Software Vendors.
But these pages should not simply replace one industry name with another.
Each page should include real differences in:
- risk profile;
- buyer concerns;
- common attack surface;
- procurement requirements;
- compliance context;
- technical environment;
- proof and examples.
This makes the pages useful rather than thin SEO variations.
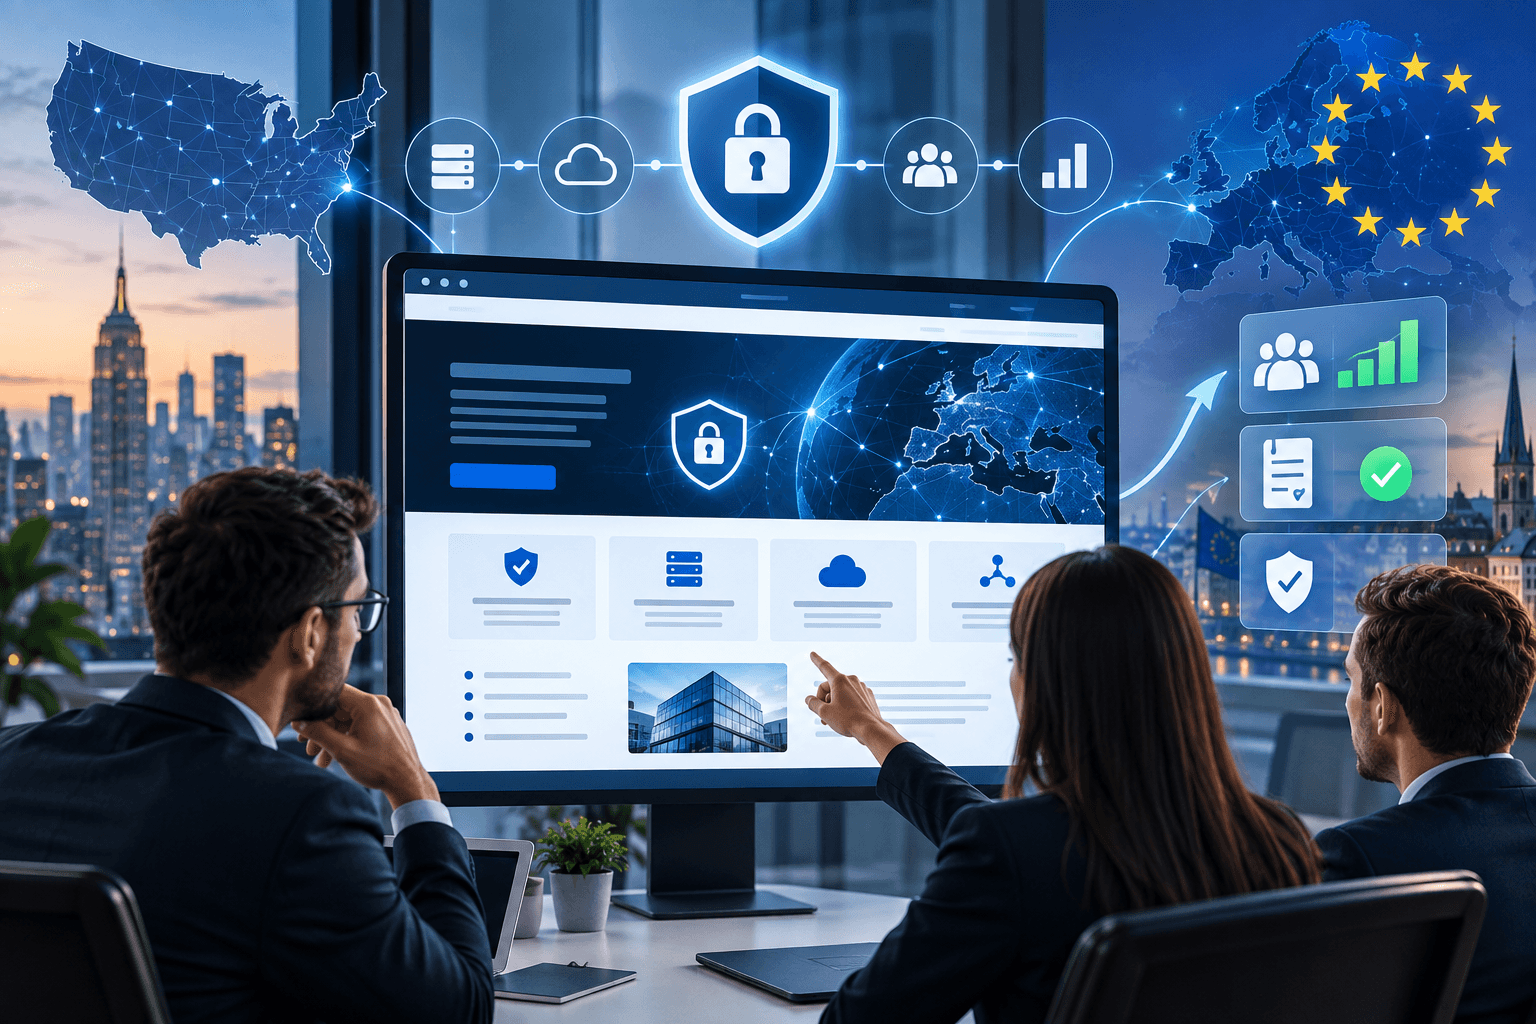
US and European Buyers May Need Different Trust Signals
A company targeting both the United States and Europe should avoid assuming that one generic presentation will work equally well for every market.
The core service can remain the same, but trust and buying context may differ.
European visitors may pay more attention to:
- data processing;
- privacy;
- regulatory context;
- service location;
- contract structure;
- cross-border data handling.
US enterprise buyers may place more emphasis on:
- vendor capability;
- speed of engagement;
- scalability;
- business risk;
- technical depth;
- enterprise procurement readiness.
The website does not necessarily need a separate domain for each market.
But important service and market pages can address these differences explicitly.
Build Content Around Security Problems, Not Generic SEO Topics
A cybersecurity blog should not exist simply to publish weekly articles.
The best content supports commercial intent.
Useful problem-led topics may include:
- Why a SaaS Company Fails an Enterprise Security Review;
- What to Fix Before a Customer Requests a Penetration Test;
- Why Vulnerability Scanning Is Not the Same as Penetration Testing;
- How to Prepare a Web Application for External Security Testing;
- What Security Evidence Enterprise Buyers Expect from SaaS Vendors;
- When a Growing Company Needs an External Security Assessment.
These topics attract buyers who already have a real problem.
Each article should then lead naturally to an appropriate service or consultation path.
Avoid Fear-Based Conversion Tactics
Security marketing often relies too heavily on fear.
Warnings about breaches, fines, attacks, and business failure can attract attention, but excessive fear can reduce credibility.
Enterprise buyers usually respond better to:
- clear risk explanation;
- practical evidence;
- structured methodology;
- specific mitigation options;
- professional communication.
The website should make the risk understandable without turning every page into a disaster scenario.
This positioning is especially important for companies selling long-term consulting or managed security relationships.
Your CTA Should Match the Buying Stage
“Contact Us” is functional, but cybersecurity buyers may respond better to a more specific first step.
Examples include:
- Discuss Your Security Assessment;
- Request a Penetration Testing Scope Review;
- Talk to a Security Consultant;
- Review Your Current Security Testing Requirements;
- Discuss Enterprise Security Readiness.
The CTA should not promise a free audit unless the company genuinely provides one.
For expensive services, the objective is usually to begin a qualified conversation rather than force an immediate purchase.
The Contact Form Should Help Qualify Enterprise Leads
A cybersecurity company does not need every visitor to submit a form.
It needs relevant prospects.
A useful inquiry form may request:
- name;
- company;
- business email;
- website;
- service required;
- environment or project type;
- short description of the requirement;
- preferred timeline where relevant.
Avoid asking for sensitive technical information through a normal website form.
The initial form should provide enough information to qualify the conversation without encouraging visitors to share confidential data unnecessarily.
Technical Quality of the Website Is Part of the Sales Message
This matters more for cybersecurity companies than for many other industries.
If a security company’s own website has obvious problems, it can undermine confidence immediately.
The website should be reviewed for:
- HTTPS configuration;
- software updates;
- form security;
- spam protection;
- broken scripts;
- cookie and privacy implementation;
- page performance;
- mobile usability;
- unnecessary exposed technical information;
- outdated plugins or modules.
A potential client may never inspect the website deeply, but technical sloppiness is particularly damaging when the product being sold is security expertise.
Track Qualified Opportunities, Not Only Form Submissions
Cybersecurity projects can have high value and long sales cycles.
That means website reporting should eventually distinguish between a lead and a qualified opportunity.
Useful measurement may include:
- landing page;
- traffic source;
- service requested;
- form submission;
- discovery call booked;
- qualified opportunity;
- proposal issued;
- closed project.
Connecting website analytics with CRM outcomes makes it possible to understand which pages actually contribute to revenue.
A page producing three strong enterprise opportunities may be more valuable than an article producing thousands of irrelevant visitors.
Cybersecurity Website Lead Generation Checklist
- The homepage clearly identifies the target client and security problem.
- Priority services have dedicated commercial pages.
- Technical language is understandable to multiple buyer roles.
- Methodology is explained clearly.
- Case studies demonstrate how problems were handled.
- Industry pages contain genuinely industry-specific content.
- US and European trust concerns are addressed where relevant.
- Content targets real security problems, not broad traffic topics.
- CTAs match the service and buying stage.
- Forms help qualify leads without requesting unnecessary sensitive information.
- The website itself meets a high technical quality standard.
- Commercial pages receive internal links from relevant content.
- Conversion tracking is connected to meaningful business outcomes.
- Marketing is based on evidence rather than exaggerated fear.
FAQ
Should a cybersecurity website target broad keywords such as cybersecurity services?
Broad keywords can be useful strategically, but they are highly competitive and often poorly qualified. Newer or smaller providers usually have a better opportunity with narrower combinations of service, industry, technology, risk, and buyer intent.
What should a cybersecurity service page include?
It should explain the problem, ideal client, scope, methodology, deliverables, proof, typical engagement process, and a clear next step.
Can cybersecurity companies publish case studies without exposing sensitive information?
Yes. Case studies can be anonymized and focused on the type of problem, methodology, risk category, remediation process, and business outcome without revealing confidential technical details.
Should US and European traffic use separate landing pages?
Not automatically. Separate pages make sense when search intent, regulatory context, trust requirements, service offering, or messaging differs enough to justify a distinct page.
Conclusion
A cybersecurity company’s website has to do more than look secure and professional.
It needs to demonstrate technical maturity, translate security problems into business relevance, support multiple enterprise stakeholders, and give serious prospects enough confidence to begin a conversation.
For companies targeting the United States and Europe, narrow service positioning, technical case studies, industry-specific pages, strong proof, and clear qualification paths can be more valuable than trying to attract broad cybersecurity traffic.
If your cybersecurity company has strong technical expertise but the website does not generate enough qualified enterprise conversations, our team can review the website structure, service pages, positioning, SEO architecture, and conversion paths before recommending a redesign.
You may also want to read our articles about B2B brochure website conversion, internal linking audits, thin service pages, and pre-redesign technical audits.